EASM
Map your internet-facing assets and track changes to your external attack surface.
ScopeDomains, IP addresses and exposed services
AUTODIT.IO · Cybersecurity platform
EASM, pentesting, code audit and cloud / identity audit: four products together to assess your risks, prioritize fixes and document your audits.
Our solutions
Map your internet-facing assets and track changes to your external attack surface.
ScopeDomains, IP addresses and exposed services
Assess the security of your applications and services through penetration testing.
ScopeApplications and services to test
Analyze source code to identify security flaws and exposed secrets.
ScopeSource code and secrets
Review cloud configurations, identities and access permissions to identify risks.
ScopeCloud configurations, identities and access permissions
How it works
Choose the product and scope to assess: external exposure, applications, source code, or cloud environments and identities.
Run the analyses suited to your scope, then qualify vulnerabilities, misconfigurations and risky access permissions.
Organize fixes, track remediation and share results with your technical teams and decision-makers.
The results
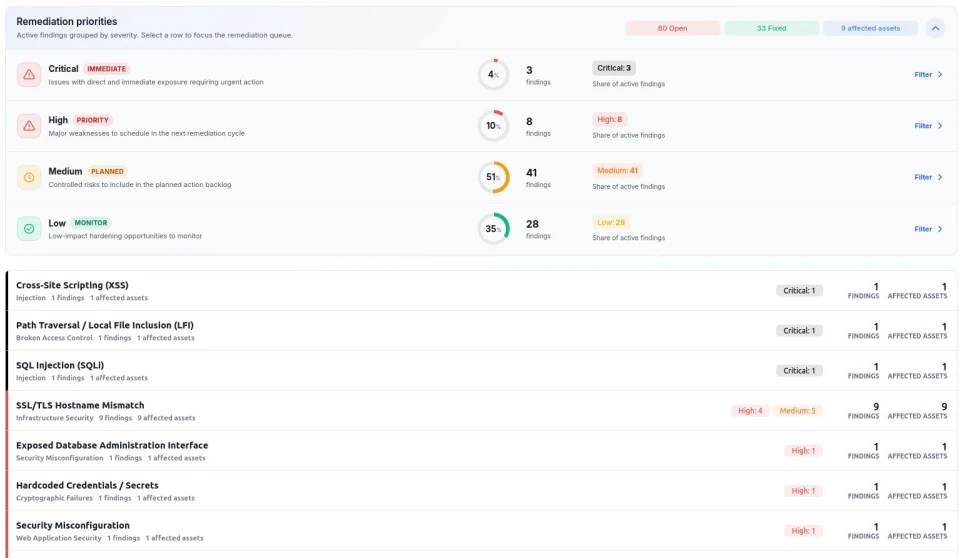
Review audit findings, their context and useful recommendations to organize remediation.
PDF, Excel and PowerPoint exports to share findings and next steps. Available formats depend on the module and access permissions.
Technical checks and reports that support NIS2, DORA, ISO 27001, GDPR, PCI-DSS and SOC 2 work. These materials do not constitute compliance certification.
REST API and MCP server. Jira and ServiceNow require suitable configuration and permissions. SIEM connections, including Splunk, Elastic and QRadar, may require a connector or custom development.
Describe your perimeter and expectations. We will help prepare a demonstration and discuss options suited to your needs.